Aviation Security & Compliance: Turning Regulations into Measurable Protection
Aviation security is not just about protecting airports. It is about protecting the entire aviation ecosystem. 🌐
From passenger screening and aircraft access to air cargo protection and cybersecurity, aviation security relies on defined controls, regulatory oversight, and verifiable compliance.
But how do aviation organisations know whether their security measures are working as intended?
The answer lies in combining regulatory compliance with effective monitoring, reliable data, and continuous oversight.
🛡️ 1. ICAO Annex 17: The International Foundation
The International Civil Aviation Organization (ICAO) establishes international Standards and Recommended Practices (SARPs) for aviation security through Annex 17 to the Chicago Convention.
Its framework addresses the prevention of unlawful interference with civil aviation.
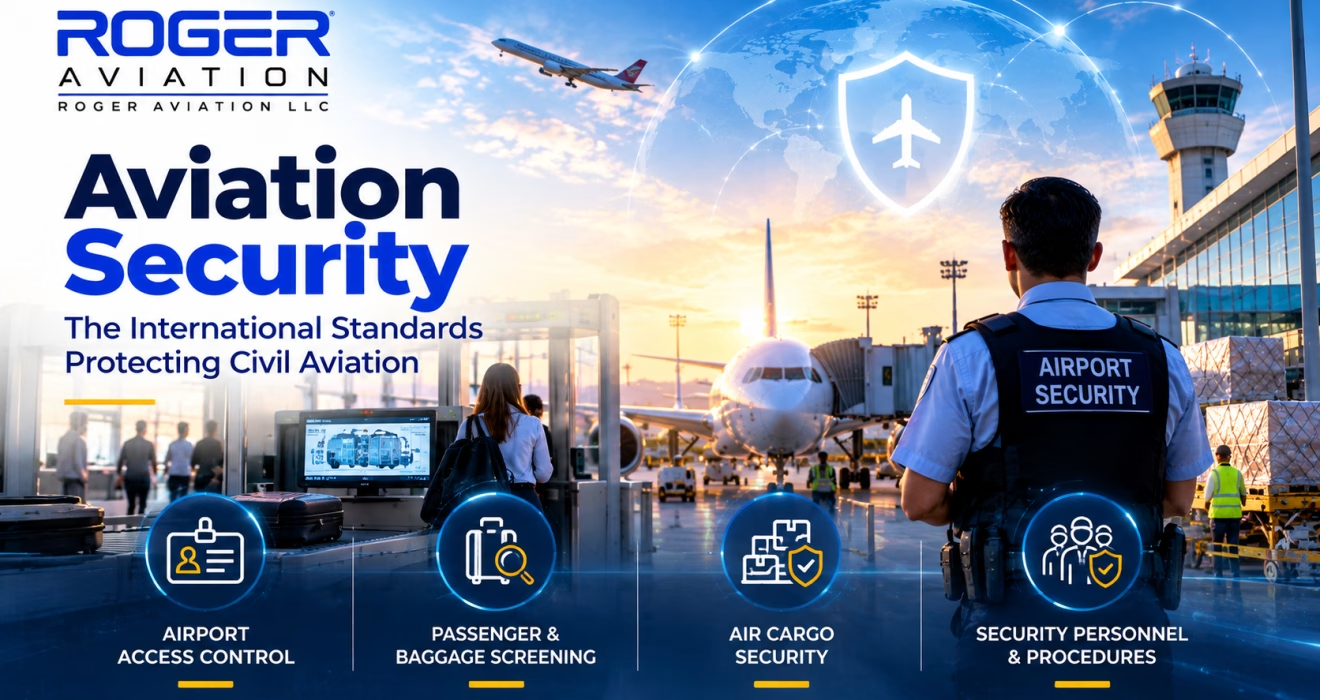
Key areas include:
🔐 Access Control: Protecting restricted airport areas from unauthorised access.
🧳 Security Screening: Applying required security controls to passengers, baggage, and other relevant items.
📦 Cargo Security: Protecting air cargo and mail through applicable security procedures.
👥 Personnel Security: Establishing appropriate personnel-related security measures and training.
🌐 Cybersecurity: Addressing cyber threats that could affect civil aviation security.
ICAO provides the international framework, while individual states establish and enforce applicable national requirements.
📊 2. Compliance Must Be Measurable
Having a security policy is not the same as demonstrating compliance.
Aviation organisations need documented processes, evidence of implementation, appropriate oversight, and corrective action when deficiencies are identified.
Data can help organisations monitor compliance through indicators such as:
📋 Audit Findings: Number and classification of findings identified during security audits.
⏱️ Corrective Action Closure: Time taken to address identified deficiencies.
🎓 Training Compliance: Completion of required security training within applicable deadlines.
🔑 Access Control Exceptions: Recorded exceptions requiring investigation or review.
📑 Documentation Accuracy: Completeness and validity of required records, approvals, and security documentation.
These are examples of possible internal monitoring indicators, not universal regulatory thresholds. Their definitions, targets, and reporting requirements must reflect the applicable regulations and organisational security programme.
The objective is to turn compliance evidence into actionable information.
💻 3. Why Digital Systems Matter
Aviation security involves multiple teams, processes, and records. Managing this information effectively is essential for oversight.
Digital systems can support compliance by helping organisations:
✅ Maintain traceable records of inspections, audits, and corrective actions.
✅ Monitor training validity and renewal deadlines.
✅ Identify overdue compliance activities.
✅ Track access authorisations and approval status.
✅ Generate reports for management review and regulatory oversight.
However, digitalisation alone does not establish compliance. Systems must be appropriately configured, access-controlled, maintained, and aligned with applicable requirements.
🔍 4. Aviation Cybersecurity: The Expanding Compliance Landscape
Aviation increasingly depends on connected digital infrastructure, making cybersecurity an important part of the wider security framework.
ICAO explicitly addresses aviation cybersecurity in its security work, including provisions under Annex 17.
Security considerations can extend to information systems, operational technology, third-party access, and the protection of sensitive information.
Organisations should identify relevant cyber risks, establish appropriate controls, document responsibilities, and follow applicable regulatory requirements.
Data access, system changes, security incidents, and unresolved vulnerabilities can be monitored through defined processes where appropriate.
The goal is to ensure that digital capabilities support aviation operations without introducing unmanaged security risks.
🎯 5. From Compliance Records to Better Decisions
The real value of compliance data lies in how organisations use it.
When audit findings, training records, access exceptions, and corrective actions are reviewed together, management can identify recurring issues and determine where further investigation is necessary.
For example, repeated audit findings may indicate a process weakness that requires root-cause analysis rather than another isolated correction.
This approach supports more informed oversight while keeping decisions grounded in documented evidence.
Aviation security requires more than policies on paper. It requires controls that are implemented, monitored, documented, and reviewed.
At Roger Aviation, we recognise the role of technology, data integration, and digital transformation in supporting aviation organisations as they manage complex operational and compliance requirements.
✈️ Better visibility. Stronger oversight. More informed decisions.
🌐 Explore Roger Aviation: https://roger.ae
💬 How can better data visibility improve security compliance across the aviation industry?
Share your perspective in the comments.
📚 Official References
- International Civil Aviation Organization (ICAO), Annex 17: Aviation Security.
- ICAO, Aviation Cybersecurity.
- European Commission, Aviation Security Regulations.
Disclaimer: This article is intended for educational and informational purposes only .
Please consult the latest official publications and applicable national aviation security regulations for authoritative guidance.
#RogerAviation #AviationSecurity #ICAO #AviationCompliance #AviationCybersecurity #AviationTechnology #DataAnalytics #DigitalTransformation #AirportSecurity #RegulatoryCompliance